
ShriD5@ShriD5
ShriD5/claude-mods/tree/main/secret-guard
通过 tool.call 钩子阻止 Write、Edit、MultiEdit、NotebookEdit 和 Bash 重定向把看似真实的凭据写入文件,同时允许占位符、开发默认值和 .env 文件。
ShriD5/claude-mods/tree/main/secret-guard
secret-guard 添加 tool.call 钩子,检查文件工具准备写入的文本以及 Bash 命令重定向到文件的内容;发现看似真实的凭据就拒绝调用。它检测 AWS、Anthropic/OpenAI、GitHub、Slack、Stripe、Google 密钥、私钥块以及带内嵌密码的数据库 URL。占位符(xxxx、process.env.X、EXAMPLE 密钥)、开发默认值(localhost、example.com、postgres:postgres)、文件中已有的秘密和 .env 系列文件会放行,但 .env.example/.sample/.template 仍受保护。CLAUDE.md 和 AGENTS.md 会接受更严格检查。被阻止时会告诉 Claude 发现了什么及所在行,并要求改用环境变量,不回显秘密。使用 claude --plugin-dir ./secret-guard 或市集安装,并运行 /secret-guard 查看按类型统计的阻止结果。
请先查看作者 README 确认 marketplace 和插件名称;命令可能随仓库结构改变。
claude plugin marketplace add ShriD5/claude-mods
claude plugin install secret-guard
Stops Claude from writing secrets into files. When a Write, Edit, MultiEdit or NotebookEdit would put a real-looking credential into a file, or a Bash command would echo, printf, tee or heredoc one into a file, the call is refused. Claude is told what it found and on which line, and to read the value from an environment variable instead, with the value kept in a gitignored .env. The secret itself is never repeated back.
🔒 secret-guard blocked a GitHub token in config.ts
It catches:
AKIA…, ASIA…)sk-ant-…), OpenAI keys (sk-proj-…, legacy sk-…), and other long sk-… keysghp_, gho_, ghu_, ghs_, ghr_, github_pat_)xoxb-, xoxp-, …) and Slack webhook URLssk_live_, rk_live_)AIza…)-----BEGIN … PRIVATE KEY----- with a key body)postgres://, mysql://, mongodb+srv://, redis://, amqp://)It lets these through:
xxxx, your-key-here, <api-key>, ${VAR}, process.env.X, AKIA…EXAMPLE, low-variety strings.localhost or a docker service name, documentation hosts like example.com, and default passwords like postgres:postgres..env, .env.local, .env.production and .dev.vars, which is where the deny message tells Claude to put secrets. .env.example, .env.sample and .env.template are still guarded, because those get committed.CLAUDE.md and AGENTS.md get extra-strict checks. In those files any credential-named assignment with a random-looking value (api_key: "q8Zr…") is blocked too. The deny reason also tells Claude why: these files are often committed and public, and in a public sample of 25,784 CLAUDE.md files, 275 contained real-looking secrets.
Run /secret-guard to see how many secrets it has blocked so far, broken down by type.
claude --plugin-dir ./secret-guard
or add this repo as a marketplace and install it with /plugin.
None. The rules live in hooks/detect.ts. Each one is a regex for a format a real service issues, followed by placeholder checks.
A tool.call hook reads the text a file tool is about to write, or the files a Bash command redirects into, and runs the detector on it. If anything new turns up, it answers { deny } so the tool never runs. The running count is kept in $.store.
这是你的项目吗?把这个徽章放进 README 或网站,链接回本页。

一个 Claude Code 插件,可在你录制时在屏幕上遮挡机密信息、个人详细信息和商业数据,并保持私密文件关闭,提供 /rec、/rec strict、/rec off 和 /rec config 命令。

pii-guard Mod(Claude Mods 前端)

让密钥、电子邮件地址和 IP 地址不进入会话记录:进入时替换为稳定的占位符,进入工具调用时再恢复真实值。

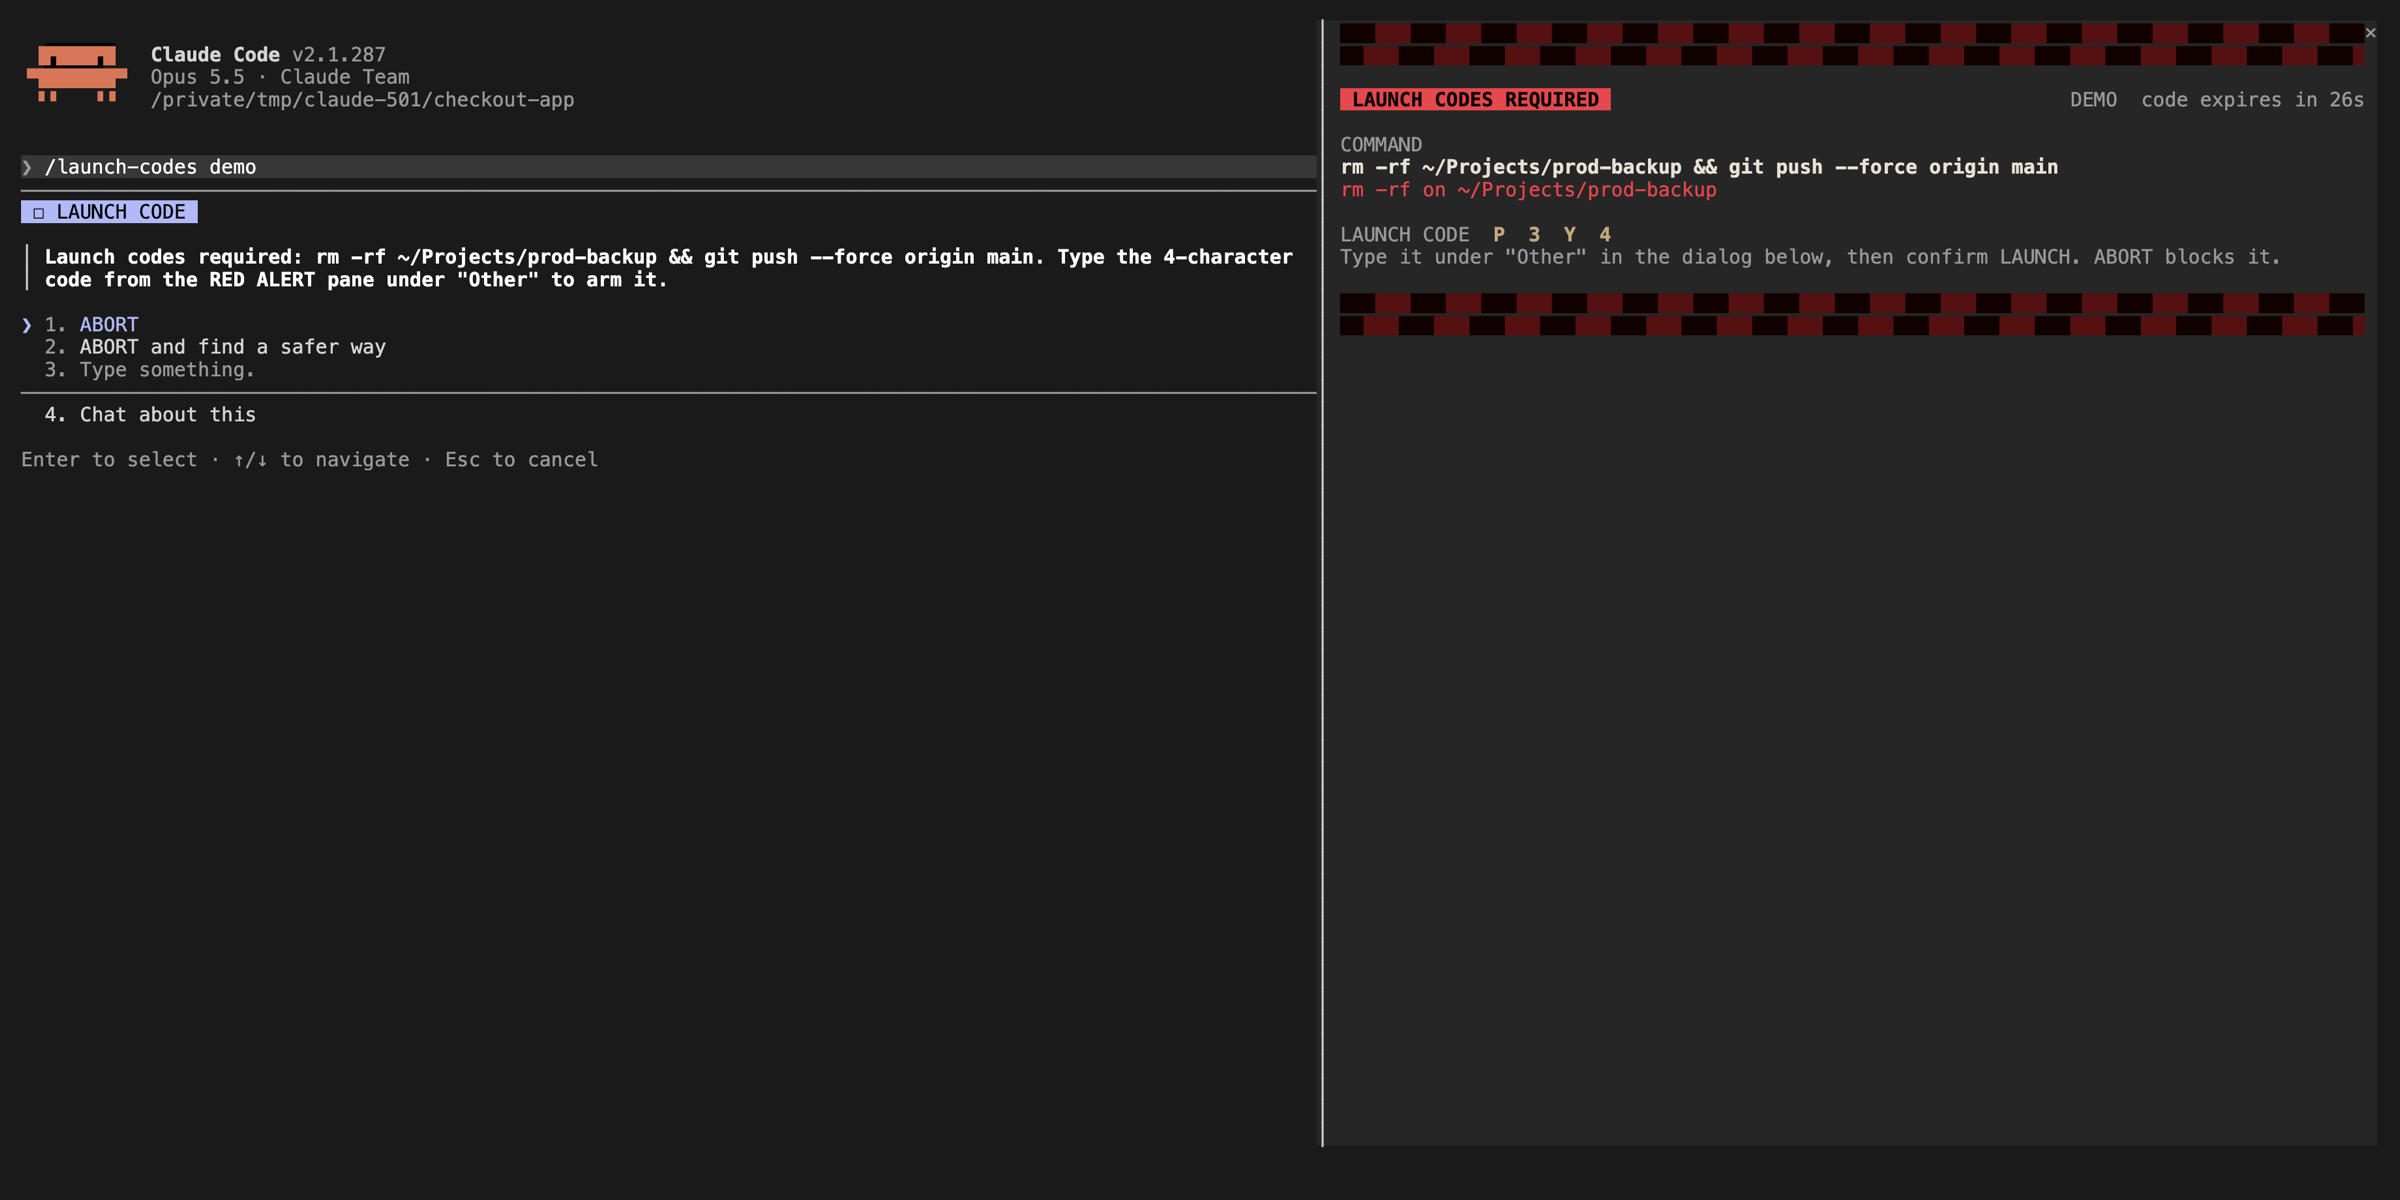
为危险命令增加一次性确认码,帮助避免误执行。

一个 Claude Code 防护 mod,会拒绝 Edit、Write 和 NotebookEdit 访问机密位置(dotenv 文件、私钥、~/.ssh、~/.aws、~/.gnupg、pass 存储)以及带有凭据形态的内容,包括 URL 中的密码。它也会拒绝 Bash 写入这些路径,以及会将其打印出来的 Bash 读取操作。自带测试。

一个 Claude Code mod,会监视 Edit/Write 对 GitHub Actions 工作流的编辑;当某一步固定到了会移动的 ref(tag 或 branch)时,告诉模型应改写为对应的 commit SHA;可选的 deny 模式会在 ref 固定前阻止 git commit、push 和 merge。