
ray-amjad@ray-amjad
ray-amjad/awesome-claude-code-function-hooks/tree/main/plugins/secret-redactor
ray-amjad/awesome-claude-code-function-hooks/tree/main/plugins/secret-redactor
讓三類值不進入工作階段紀錄:機密資訊、電子郵件地址和 IP 位址。
請先啟用函式鉤子。 這是一個 Claude Code 函式鉤子, 屬於 anthropics/claude-code#91870 中提出的搶先體驗功能。 預設關閉,在啟用前此外掛不會執行任何操作。將
"env": { "CLAUDE_CODE_ENABLE_FUNCTION_HOOKS": "1" }加入~/.claude/settings.json,或用CLAUDE_CODE_ENABLE_FUNCTION_HOOKS=1 claude啟動一次工作階段。
真實值不會被銷毀,而是進入鉤子模組中僅存在於目前工作階段記憶體的保險庫,工作階段紀錄中則以預留位置替代:
ANTHROPIC_API_KEY=[REDACTED-SECRET-164d0c98]
SUPPORT_EMAIL=[REDACTED-EMAIL-6f096ff7]
EDGE_ORIGIN=[REDACTED-IP-6fc52d2b]
同一個值總會產生同一個預留位置,因此模型仍能區分不同客戶。進入工具呼叫時,預留位置會換回真實值,所以 Bash 指令或 Write 仍攜帶真實金鑰。不向磁碟寫入任何內容。保險庫隨工作階段結束而消失。
| 事件 | 作用 |
| --- | --- |
| prompt.submit | 你貼上的金鑰不會以原始值傳給模型 |
| tool.call | 在工具輸入中還原真實值,再在工具結果中隱藏。機密資訊通常從這裡進入:cat .env、用 Read 讀取設定或 API 回應 |
| prompt.context | 隱藏附加在第一則訊息上的區塊中的機密資訊。此處不處理電子郵件地址:引擎會把你的地址放入該區塊,讓模型知道它在與誰交流 |
依序進行三項偵測。
sk-ant-、ghp_、AKIA、sk_live_、whsec_、AIza、
xoxb-、JWT、Slack 或 Discord webhook、PRIVATE KEY 區塊,以及
postgres://user:pass@host 字串中的密碼。一經發現就隱藏。API_KEY=、"token":、Bearer、password: 等內容之後。四條規則減少誤判。它們共同將一個大型 Next.js monorepo 的整個已追蹤原始碼樹的命中數降到兩處,而且兩處都是真實機密資訊。
price_、prod_、cus_、promo_、
pk_live_ 等 Stripe 物件 id,以及 YouTube 頻道 id,
會顯示在儀表板和原始碼中。隱藏它們沒有保護作用。archived-modules-marker、
lesson_article_outline_open_v1、playerEventBatchV1Schema、
randomTimestampWithinLast14Days 和
META_Conv_Lookalike-Customers_FreeTrial_2024Q1 看起來都有較高熵。
但它們是詞語組合,金鑰不是由詞語組成的。API_KEY= 或 "token": 時才視為機密資訊。noreply@、@users.noreply.github.com、
文件網域(@example.com、@company.com、@test)、
預留使用者名稱(you@、name@、admin@),以及 allowEmails 中的所有項目。
將你公開的地址以 @yourdomain.com 等形式放入該選項,
讓你自己的聯絡地址保持可讀。127.0.0.1:3000:迴路、10.x、
192.168.x、172.16-31.x、鏈路本地、電信業者級 NAT、多播、
基準測試範圍及 RFC 5737 文件範圍。設定 redactPrivateIps 也可隱藏這些位址。在使用者設定的 pluginConfigs 下依外掛設定。
| 選項 | 預設值 | 作用 |
| --- | --- | --- |
| secrets | true | 隱藏機密資訊 |
| pii | true | 隱藏電子郵件和 IP 位址 |
| restoreInToolInputs | true | 工具執行前還原真實值 |
| notify | true | 工具列顯示計數,提示詞處顯示浮動通知 |
| minEntropy | 3.6 | 大小寫混合偵測的每字元位元數 |
| minLength | 24 | 大小寫混合偵測的最短 token 長度 |
| contextMinEntropy | 3.0 | 前面有金鑰名稱時的每字元位元數 |
| redactPrivateIps | false | 同時隱藏保留範圍 |
| allow | "" | 保留原樣的精確字串,以逗號分隔 |
| allowEmails | "" | 地址或 @domain.com,以逗號分隔 |
| allowPrefixes | "" | 額外視為公開 id 的前綴 |
| denyPrefixes | "" | 重新納入熵偵測的前綴 |
所有指令都從此儲存庫根目錄執行。
步驟 1:產生型別宣告。它們不在 git 中,因為新的 Claude Code 版本會重寫它們。
此指令寫入 tsconfig.json 所引用的 types/claude-code.d.ts:
/plugin-types
步驟 2:執行偵測器測試和外掛驗證器:
node --experimental-strip-types plugins/secret-redactor/test/detect.test.mts
claude plugin validate plugins/secret-redactor
test/detect.test.mts 有兩個清單:必須隱藏的值和必須保留的值。
修改門檻或模式,只有兩個清單都仍通過測試才算完成。
步驟 3:進行端對端試用:
claude --plugin-dir plugins/secret-redactor \
  -p "cat plugins/secret-redactor/test/fixtures/sample.env, then repeat the values back"
請先查看作者 README,確認 marketplace 與外掛名稱;指令可能隨儲存庫結構而變動。
claude plugin marketplace add ray-amjad/awesome-claude-code-function-hooks
claude plugin install secret-redactor
Keeps three classes of value out of the session transcript: secrets, email addresses and IP addresses.
Turn function hooks on first. This is a Claude Code function hook, the early-access feature proposed in anthropics/claude-code#91870. It is off by default, and this plugin does nothing until you turn it on. Add
"env": { "CLAUDE_CODE_ENABLE_FUNCTION_HOOKS": "1" }to~/.claude/settings.json, or start one session withCLAUDE_CODE_ENABLE_FUNCTION_HOOKS=1 claude.
The value is not destroyed. It goes into a vault that lives in the hooks module, in memory, for the session, and the transcript gets a placeholder in its place:
ANTHROPIC_API_KEY=[REDACTED-SECRET-164d0c98]
SUPPORT_EMAIL=[REDACTED-EMAIL-6f096ff7]
EDGE_ORIGIN=[REDACTED-IP-6fc52d2b]
The same value always mints the same placeholder, so the model can still tell
one customer from another. The placeholder is swapped back for the real value
on the way into a tool call, so a Bash command or a Write still carries the
real key. Nothing is written to disk. The vault dies with the session.
| Event | What it does |
| --- | --- |
| prompt.submit | A key you paste never reaches the model as itself |
| tool.call | Puts real values back into the tool's input, then hides them again in the tool's result. This is where a secret usually arrives: a cat .env, a Read of a config, an API answer |
| prompt.context | Hides secrets in the blocks attached to the first message. Emails are left alone there: the engine puts your own address in that block so the model knows who it is talking to |
Three tests, in order.
sk-ant-, ghp_, AKIA, sk_live_, whsec_, AIza,
xoxb-, a JWT, a Slack or Discord webhook, a PRIVATE KEY block, the
password inside a postgres://user:pass@host string. Hidden on sight.API_KEY=, "token":, Bearer, password: and the like.Four rules stop the noise. Together they take a large Next.js monorepo down to two hits across its whole tracked source tree, and both are real secrets.
price_, prod_, cus_, promo_,
pk_live_ and the rest of Stripe's object ids, and a YouTube channel id, are
printed in dashboards and in source. Hiding them protects nothing.archived-modules-marker,
lesson_article_outline_open_v1, playerEventBatchV1Schema,
randomTimestampWithinLast14Days and
META_Conv_Lookalike-Customers_FreeTrial_2024Q1 all read as high entropy.
They are word lists. A key is not built out of words.API_KEY= or "token": sits in front of it.noreply@, @users.noreply.github.com,
documentation domains (@example.com, @company.com, @test),
placeholder local parts (you@, name@, admin@), and anything in
allowEmails. Put your own published addresses in that option, as
@yourdomain.com, so your own contact address stays readable.127.0.0.1:3000 is everywhere in dev: loopback, 10.x,
192.168.x, 172.16-31.x, link-local, carrier-grade NAT, multicast, the
benchmarking range, and the RFC 5737 documentation ranges. Set
redactPrivateIps to hide those too.Set them per plugin under pluginConfigs in your user settings.
| Option | Default | What it does |
| --- | --- | --- |
| secrets | true | Hide secrets |
| pii | true | Hide emails and IP addresses |
| restoreInToolInputs | true | Put the real value back before a tool runs |
| notify | true | Count on the tool row, toast on a prompt |
| minEntropy | 3.6 | Bits per character for the mixed-case test |
| minLength | 24 | Shortest token the mixed-case test looks at |
| contextMinEntropy | 3.0 | Bits per character when a key name sits in front |
| redactPrivateIps | false | Hide reserved ranges too |
| allow | "" | Exact strings to leave alone, separated by commas |
| allowEmails | "" | Addresses, or @domain.com, separated by commas |
| allowPrefixes | "" | Extra id prefixes to treat as public |
| denyPrefixes | "" | Prefixes to put back under the entropy test |
Run every command from the root of this repo.
Step 1. Make the type declarations. They are not in git, because a new Claude
Code release rewrites them. This command writes types/claude-code.d.ts, which
tsconfig.json points at:
/plugin-types
Step 2. Run the detector test and the plugin validator:
node --experimental-strip-types plugins/secret-redactor/test/detect.test.mts
claude plugin validate plugins/secret-redactor
test/detect.test.mts holds two lists: values that must be hidden and values
that must be kept. A change to a threshold or a pattern is only finished when
both still pass.
Step 3. Try it end to end:
claude --plugin-dir plugins/secret-redactor \
  -p "cat plugins/secret-redactor/test/fixtures/sample.env, then repeat the values back"
這是你的專案嗎?把這個徽章放進 README 或網站,連回本頁。

pii-guard 外掛(Claude Mods 前端)

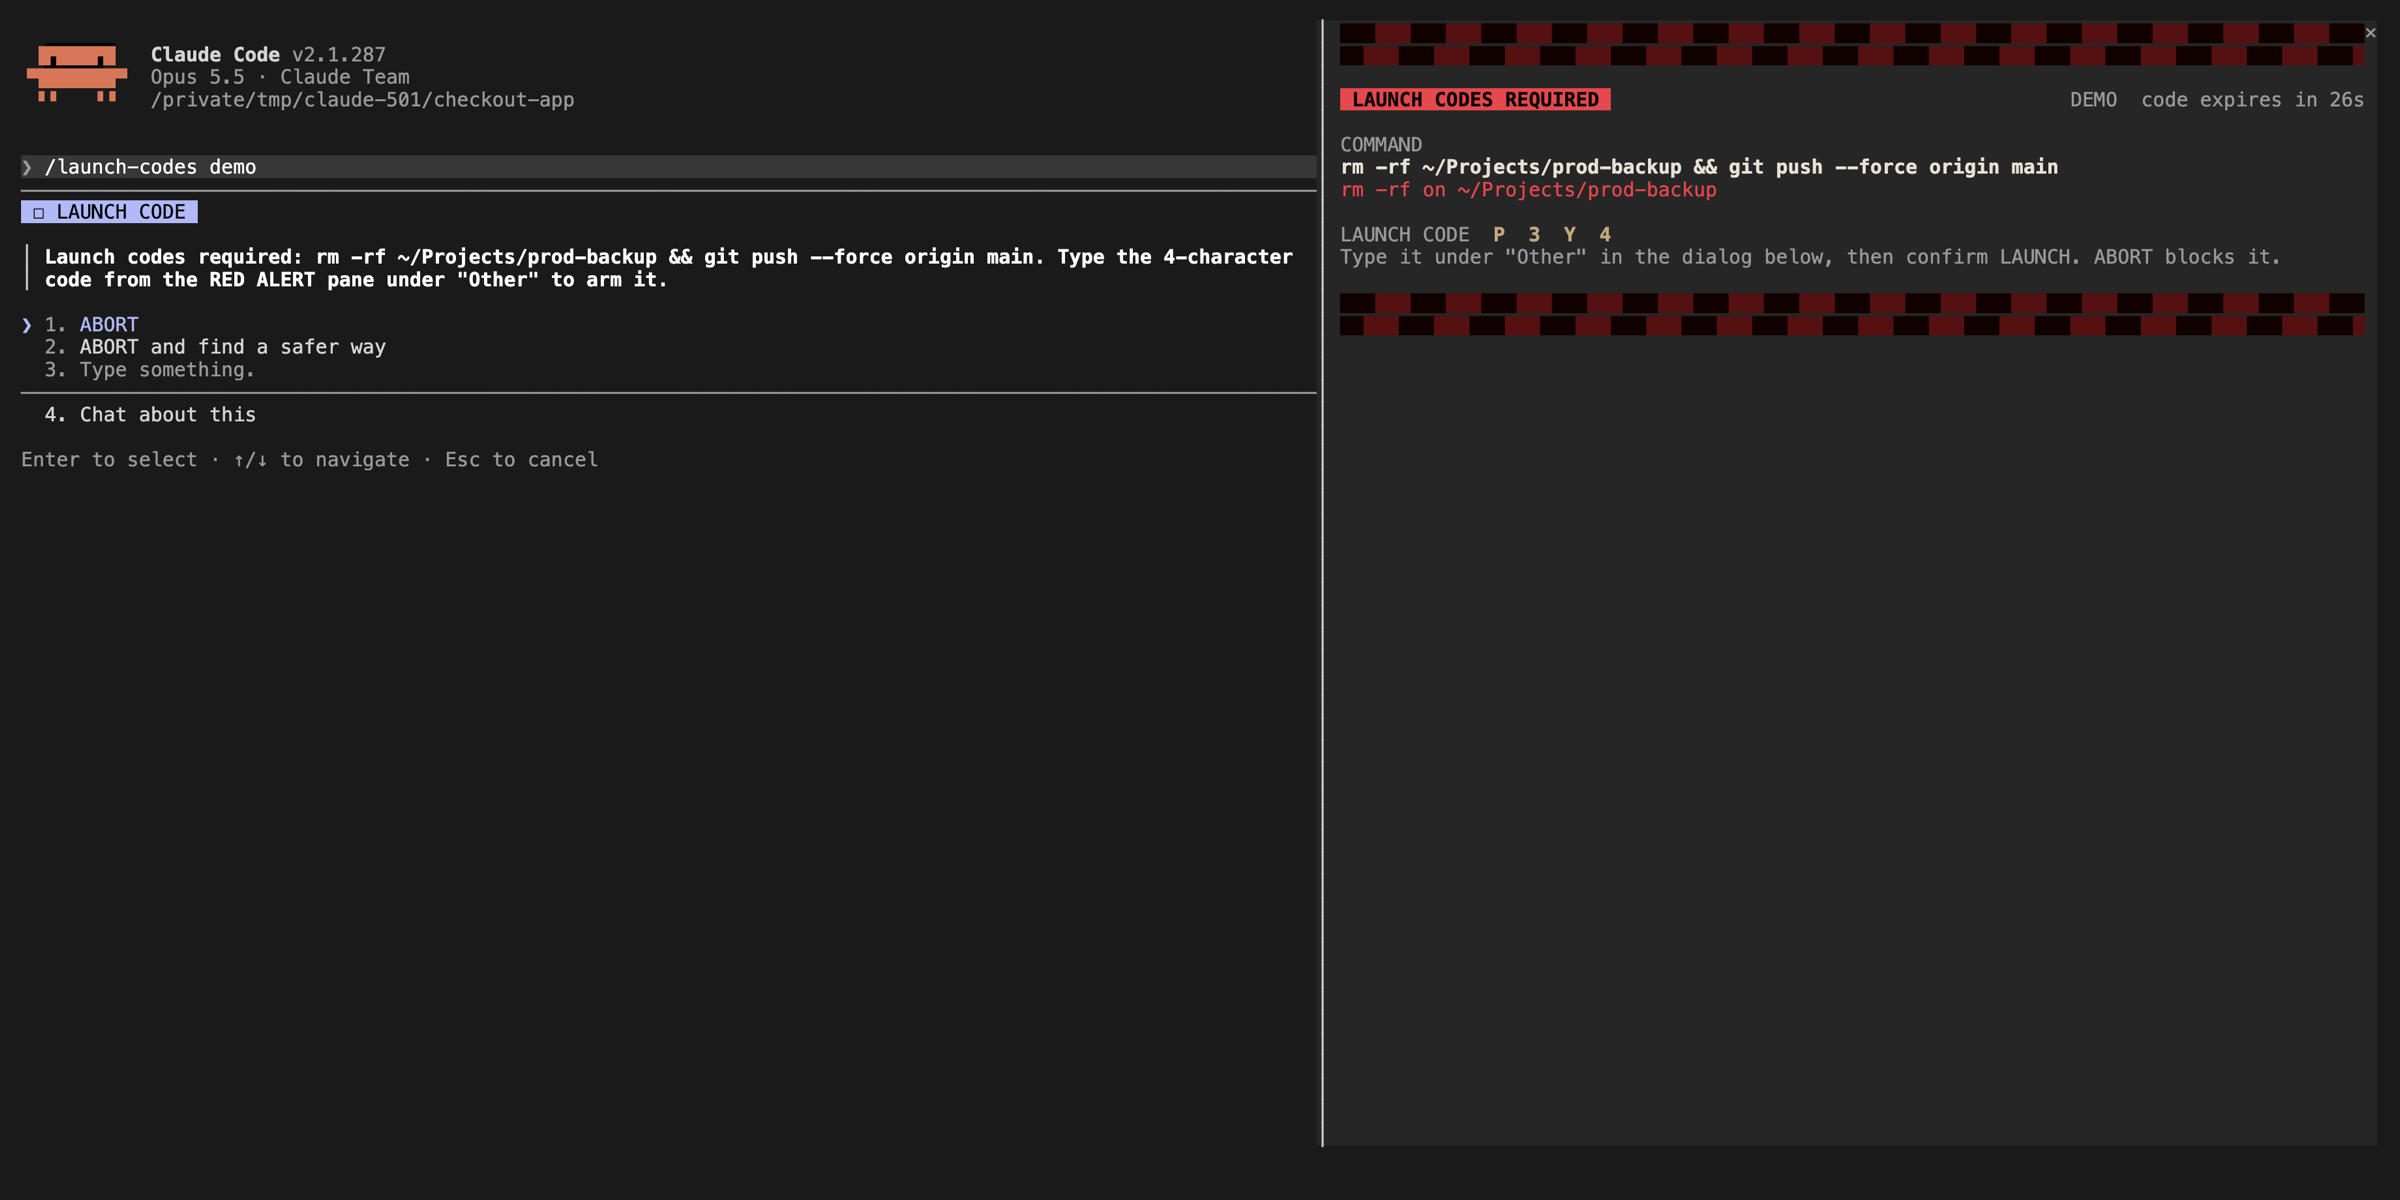
執行危險指令前要求一次性確認碼,降低誤操作的機會。

一個 Claude Code 防護 mod,會拒絕 Edit、Write 和 NotebookEdit 存取機密位置(dotenv 檔案、私密金鑰、~/.ssh、~/.aws、~/.gnupg、pass 儲存區)以及帶有憑證形態的內容,包括 URL 中的密碼。它也會拒絕 Bash 寫入這些路徑,以及會把它們印出的 Bash 讀取。內含自己的測試。

一個 Claude Code mod,會監看 Edit/Write 對 GitHub Actions 工作流程的編輯;當某一步固定到會變動的 ref(tag 或 branch)時,告訴模型應改寫成對應的 commit SHA;可選的 deny 模式會在 ref 固定前阻擋 git commit、push 和 merge。

Baselane mods 中的 Claude Code guard,會在指令列印環境變數、回顯敏感變數或將本機資料送到遠端主機前先詢問。

Claude Code 的可點擊安全規則:阻止 rm -rf、force-push、批次 kubectl 刪除、秘密檔案存取、sudo 和網路調用,具有預設和 jail-to-project 模式。