
mashabek@mashabek
mashabek/claude-mods/tree/main/plugins/secret-mask
mashabek/claude-mods/tree/main/plugins/secret-mask
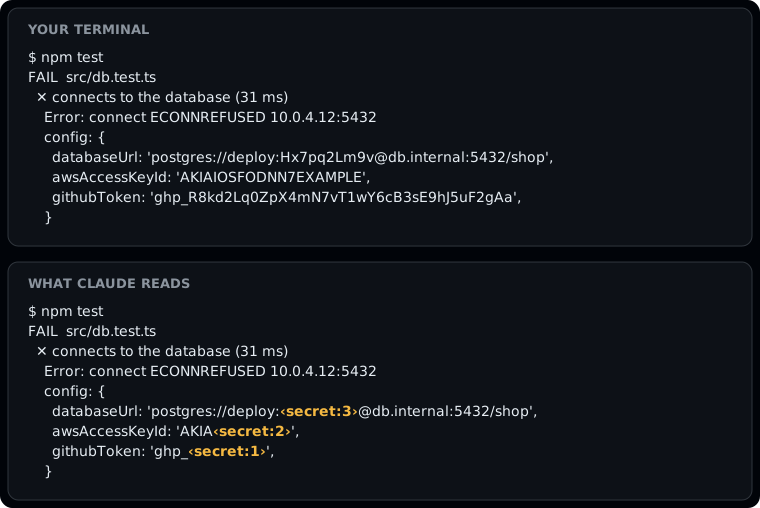
在 Claude 讀取前遮蓋工具輸出、檔案讀取結果和提示中的機密。Claude 看到的是 ‹secret:1›,而畫面仍顯示實際值。

PreToolUse hook 只能阻擋指令,而此外掛會讓指令繼續執行並遮蓋輸出。
已使用 Claude Code 2.1.288 測試。Function hook 處於搶先體驗階段,後續版本可能使其失效。
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask@claude-mods
| | |
|---|---|
| /secret-mask | 顯示狀態、讀取過的檔案以及被遮蓋的內容。絕不輸出值。 |
| /secret-mask on, off | 開啟或關閉遮蓋。設定會跨工作階段記住。 |
| /secret-mask rescan | 編輯 .env 後重新讀取機密檔案。 |
一旦有內容被遮蓋,狀態列會顯示 🔒 3 masked。
.env 檔案、~/.aws/credentials、~/.npmrc、~/.netrc、~/.pgpass,以及名稱類似 *_TOKEN、*_SECRET 或 *_PASSWORD 的環境變數值;無論出現在哪裡,包括 URL 編碼和 base64 副本都會處理。Authorization 標頭,以及 user:pass@host URL 中的密碼。apiKey = "..." 或 SESSION_SECRET=...。提交雜湊、UUID、路徑、process.env.X 和 ${DB_PASS} 之類的預留位置會保持不變。它不進行網路或模型呼叫,也沒有相依性。值只保存在記憶體中。整個外掛在 hooks/ 中約 320 行,包含 23 個測試。
請先查看作者 README,確認 marketplace 與外掛名稱;指令可能隨儲存庫結構而變動。
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask
Masks secrets in tool output, file reads and prompts before Claude reads them. Claude sees
‹secret:1›, and your screen still shows the real value.
A PreToolUse hook could only block that command. This lets it run and masks the output.
Tested with Claude Code 2.1.288. Function hooks are early access, so a later release may break it.
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask@claude-mods
| | |
|---|---|
| /secret-mask | Status, which files were read, and what was masked. Never prints a value. |
| /secret-mask on, off | Turns masking on or off. Remembered across sessions. |
| /secret-mask rescan | Rereads secret files after you edit a .env. |
The status line shows 🔒 3 masked once something has been masked.
.env files, ~/.aws/credentials, ~/.npmrc, ~/.netrc,
~/.pgpass, and environment variables named like *_TOKEN, *_SECRET or *_PASSWORD,
wherever they show up, including URL-encoded and base64 copies.Authorization headers, and passwords in user:pass@host URLs.apiKey = "..." or SESSION_SECRET=....Commit hashes, UUIDs, paths, process.env.X and placeholders like ${DB_PASS} are left alone.
It makes no network or model calls and has no dependencies. Values are only held in memory.
The whole thing is about 320 lines in hooks/, with 23 tests.

面向 ruflo 的 AgentBBS 跨主機代理程式聯邦(ADR-164)。第 1 階段提供房間協調:federation_bbs_register / federation_bbs_publish / federation_bbs_watch / federation_bbs_human_join。第 2 階段(v3.40.0)加入經簽署的跨主機聯邦:federation_bbs_identity(持續儲存的 Ed25519 節點身分)、federation_bbs_peer_add(以 nodeId + 公開金鑰釘選對等節點)、federation_bbs_peers(稽核/解除釘選)、federation_bbs_serve(唯讀提取端點),以及 federation_bbs_sync(提取已釘選的對等節點,合併所有通過驗證的內容)。每個合併後的信封都會根據已釘選的金鑰進行 Ed25519 驗證;未簽署、歸屬錯誤、過大或超出跳數限制的信封會被丟棄並計數。傳輸採用 HTTP 提取,可在任何網路(Tailscale、LAN、VPN、迴圈位址)上運作,不要求 tailnet。透過宣告訊息(ClaimIssued/Released/Handoff/Ack)協調工作所有權。agentbbs 位於 optionalDependencies 中;缺少該套件時,每個處理器都會優雅降級為 {degraded:true}(ADR-150 模式)。作為 mod(ADR-445 模式),它包含一個只允許收緊限制的工具防護、一個本機斜線指令,以及控制台會顯示的狀態檔案。

pii-guard 外掛(Claude Mods 前端)

Claude Code mod,會攔住有風險的 Bash 指令(rm -r、強制推送、遷移),在執行前顯示它們會刪除的內容,60 秒沒有回答後取消。
