
mashabek@mashabek
mashabek/claude-mods/tree/main/plugins/secret-mask
mashabek/claude-mods/tree/main/plugins/secret-mask
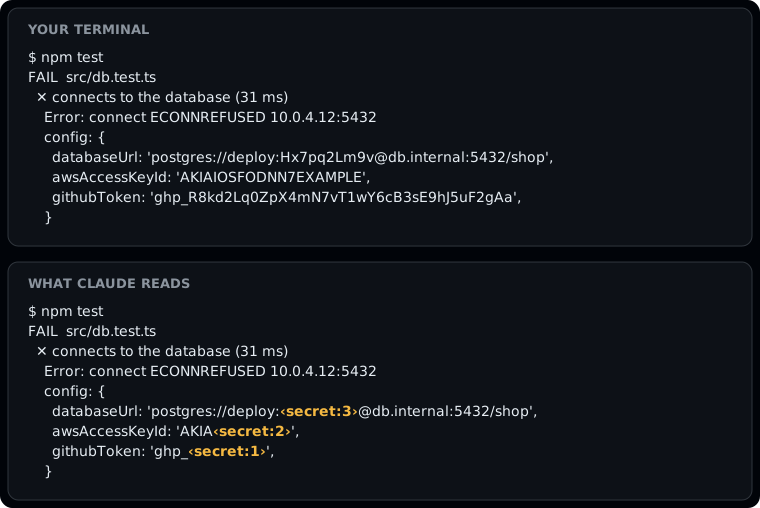
Claude가 읽기 전에 도구 출력, 파일 읽기 및 프롬프트의 비밀을 마스킹합니다. Claude에는 ‹secret:1›이 보이고 화면에는 실제 값이 계속 표시됩니다.

PreToolUse 훅은 해당 명령을 차단할 수만 있지만, 이 플러그인은 명령을 실행하고 출력을 마스킹합니다.
Claude Code 2.1.288에서 테스트되었습니다. Function hook은 얼리 액세스이므로 이후 릴리스에서 깨질 수 있습니다.
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask@claude-mods
| | |
|---|---|
| /secret-mask | 상태, 읽은 파일 및 마스킹된 항목을 표시합니다. 값은 절대 출력하지 않습니다. |
| /secret-mask on, off | 마스킹을 켜거나 끕니다. 세션 간에 기억됩니다. |
| /secret-mask rescan | .env를 편집한 뒤 비밀 파일을 다시 읽습니다. |
무언가가 마스킹되면 상태 줄에 🔒 3 masked가 표시됩니다.
.env 파일, ~/.aws/credentials, ~/.npmrc, ~/.netrc, ~/.pgpass와 *_TOKEN, *_SECRET, *_PASSWORD 같은 이름의 환경 변수 값. URL 인코딩 및 base64 복사본을 포함해 값이 나타나는 곳을 모두 처리합니다.Authorization 헤더, user:pass@host URL의 비밀번호.apiKey = "..." 또는 SESSION_SECRET=...처럼 비밀 이름에 할당된 토큰 형태의 값.커밋 해시, UUID, 경로, process.env.X 및 ${DB_PASS} 같은 플레이스홀더는 그대로 둡니다. 네트워크나 모델 호출을 하지 않으며 의존성도 없습니다. 값은 메모리에만 보관됩니다. 전체 코드는 hooks/에 약 320줄이며 테스트는 23개입니다.
먼저 작성자의 README에서 marketplace와 플러그인 이름을 확인하세요. 저장소 구조에 따라 명령어가 달라질 수 있습니다.
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask
Masks secrets in tool output, file reads and prompts before Claude reads them. Claude sees
‹secret:1›, and your screen still shows the real value.
A PreToolUse hook could only block that command. This lets it run and masks the output.
Tested with Claude Code 2.1.288. Function hooks are early access, so a later release may break it.
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask@claude-mods
| | |
|---|---|
| /secret-mask | Status, which files were read, and what was masked. Never prints a value. |
| /secret-mask on, off | Turns masking on or off. Remembered across sessions. |
| /secret-mask rescan | Rereads secret files after you edit a .env. |
The status line shows 🔒 3 masked once something has been masked.
.env files, ~/.aws/credentials, ~/.npmrc, ~/.netrc,
~/.pgpass, and environment variables named like *_TOKEN, *_SECRET or *_PASSWORD,
wherever they show up, including URL-encoded and base64 copies.Authorization headers, and passwords in user:pass@host URLs.apiKey = "..." or SESSION_SECRET=....Commit hashes, UUIDs, paths, process.env.X and placeholders like ${DB_PASS} are left alone.
It makes no network or model calls and has no dependencies. Values are only held in memory.
The whole thing is about 320 lines in hooks/, with 23 tests.

ruflo를 위한 AgentBBS 호스트 간 에이전트 페더레이션(ADR-164)입니다. 1단계에서는 룸 조정을 제공합니다: federation_bbs_register / federation_bbs_publish / federation_bbs_watch / federation_bbs_human_join. 2단계(v3.40.0)에서는 서명된 호스트 간 페더레이션을 추가합니다: federation_bbs_identity(영구 Ed25519 노드 ID), federation_bbs_peer_add(nodeId + 공개 키로 피어 고정), federation_bbs_peers(감사/고정 해제), federation_bbs_serve(읽기 전용 풀 엔드포인트), federation_bbs_sync(고정된 피어를 가져와 검증된 내용을 유니온 병합). 병합된 모든 envelope은 고정된 키에 대해 Ed25519 검증을 거칩니다. 서명되지 않았거나, 잘못 귀속되었거나, 너무 크거나, 홉 수를 초과한 envelope은 삭제되고 개수가 기록됩니다. 전송은 HTTP 풀 방식이며 어떤 네트워크(Tailscale, LAN, VPN, loopback)에서도 작동하고 tailnet은 필요하지 않습니다. 작업 소유권은 클레임 메시지(ClaimIssued/Released/Handoff/Ack)로 조정합니다. agentbbs는 optionalDependencies에 있으며 패키지가 없으면 모든 핸들러가 {degraded:true}로 graceful degradation됩니다(ADR-150 패턴). mod(ADR-445 패턴)로서 제한만 강화하는 도구 가드, 로컬 슬래시 명령, 콘솔에 표시되는 상태 파일을 제공합니다.

위험한 Bash 명령(rm -r, 강제 push, 마이그레이션)을 보류하고 실행 전에 삭제될 내용을 보여 주며 60초 동안 답이 없으면 취소하는 Claude Code mod입니다.


도구 결과가 모델에 전달되기 전에 API 키와 민감한 식별자를 숨깁니다.