
mashabek@mashabek
mashabek/claude-mods/tree/main/plugins/secret-mask
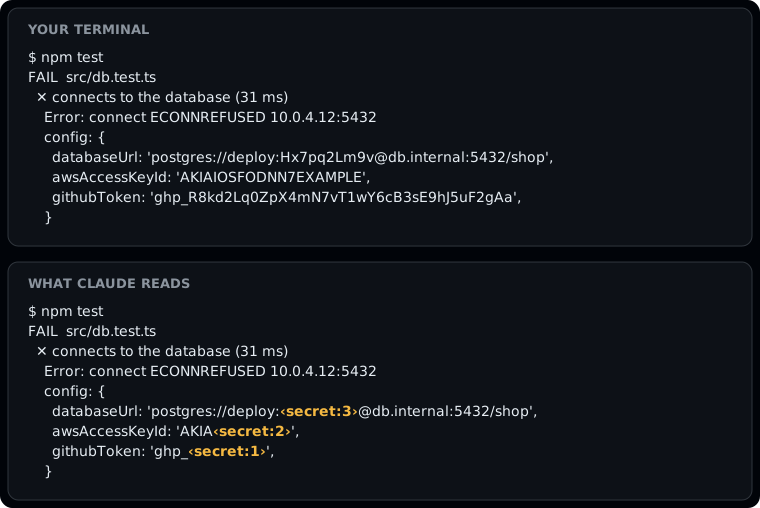
Claudeが読む前に、ツール出力とプロンプトに含まれる秘密情報(APIキー、トークン、パスワード、.envの値)をマスクします。
mashabek/claude-mods/tree/main/plugins/secret-mask
Claudeが読む前に、ツール出力、ファイル読み取り、プロンプトに含まれる秘密情報をマスクします。Claudeには‹secret:1›が見え、画面には実際の値が表示されます。

PreToolUseフックならコマンドをブロックするだけですが、これはコマンドを実行させたまま出力をマスクします。
Claude Code 2.1.288でテスト済みです。Function hookは早期アクセスのため、後のリリースで壊れる可能性があります。
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask@claude-mods
| | |
|---|---|
| /secret-mask | 状態、読み取ったファイル、マスクした内容を表示します。値は決して表示しません。 |
| /secret-mask on, off | マスクをオンまたはオフにします。セッションをまたいで記憶されます。 |
| /secret-mask rescan | .envを編集した後に秘密ファイルを再読み込みします。 |
何かをマスクすると、ステータスラインに🔒 3 maskedが表示されます。
.envファイル、~/.aws/credentials、~/.npmrc、~/.netrc、~/.pgpass、および*_TOKEN、*_SECRET、*_PASSWORDのような名前の環境変数の値。URLエンコードやbase64のコピーを含め、現れる場所でマスクします。Authorizationヘッダー、user:pass@host URLのパスワード。apiKey = "..."やSESSION_SECRET=...のように秘密らしい名前に割り当てられたトークン形式の値。コミットハッシュ、UUID、パス、process.env.X、${DB_PASS}のようなプレースホルダーはそのままです。ネットワーク通信やモデル呼び出しは行わず、依存関係もありません。値はメモリ内だけに保持されます。全体はhooks/内の約320行で、23個のテストがあります。
まず作者の README で marketplace とプラグイン名を確認してください。コマンドはリポジトリの構成によって変わる場合があります。
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask
Masks secrets in tool output, file reads and prompts before Claude reads them. Claude sees
‹secret:1›, and your screen still shows the real value.
A PreToolUse hook could only block that command. This lets it run and masks the output.
Tested with Claude Code 2.1.288. Function hooks are early access, so a later release may break it.
claude plugin marketplace add mashabek/claude-mods
claude plugin install secret-mask@claude-mods
| | |
|---|---|
| /secret-mask | Status, which files were read, and what was masked. Never prints a value. |
| /secret-mask on, off | Turns masking on or off. Remembered across sessions. |
| /secret-mask rescan | Rereads secret files after you edit a .env. |
The status line shows 🔒 3 masked once something has been masked.
.env files, ~/.aws/credentials, ~/.npmrc, ~/.netrc,
~/.pgpass, and environment variables named like *_TOKEN, *_SECRET or *_PASSWORD,
wherever they show up, including URL-encoded and base64 copies.Authorization headers, and passwords in user:pass@host URLs.apiKey = "..." or SESSION_SECRET=....Commit hashes, UUIDs, paths, process.env.X and placeholders like ${DB_PASS} are left alone.
It makes no network or model calls and has no dependencies. Values are only held in memory.
The whole thing is about 320 lines in hooks/, with 23 tests.

ruflo 向けの AgentBBS クロスホスト・エージェント連合(ADR-164)です。フェーズ 1 ではルーム調整を提供します:federation_bbs_register / federation_bbs_publish / federation_bbs_watch / federation_bbs_human_join。フェーズ 2(v3.40.0)では署名付きクロスホスト連合を追加します:federation_bbs_identity(永続的な Ed25519 ノード ID)、federation_bbs_peer_add(nodeId + 公開鍵でピアを固定)、federation_bbs_peers(監査/固定解除)、federation_bbs_serve(読み取り専用のプルエンドポイント)、federation_bbs_sync(固定したピアから取得し、検証に通った内容をユニオンマージ)。マージされたすべてのエンベロープは固定鍵に対して Ed25519 検証されます。署名なし、帰属不明、サイズ超過、またはホップ数超過のエンベロープは破棄され、件数が記録されます。転送は HTTP プルで、どのネットワーク(Tailscale、LAN、VPN、ループバック)でも動作し、tailnet は必要ありません。作業の所有権は claim メッセージ(ClaimIssued/Released/Handoff/Ack)で調整します。agentbbs は optionalDependencies に含まれ、パッケージがない場合はすべてのハンドラーが {degraded:true} に穏やかにフォールバックします(ADR-150 パターン)。mod(ADR-445 パターン)として、制限を強めるだけのツールガード、ローカルのスラッシュコマンド、コンソールが表示するステータスファイルを備えています。

危険な Bash コマンド(rm -r、強制 push、マイグレーション)を保留し、実行前に削除内容を表示し、60 秒応答がなければキャンセルする Claude Code mod です。


ツールの結果がモデルに渡る前に、API キーと機密識別子を隠します。